Bitcoin Wallets Spike to 2026 High as Coldcard Hack Fallout Spreads
Bitcoin logged 2. 27 million new wallets and 751,000 active wallets this week, its strongest onchain activity in months, as holders raced to move funds off Coldcard hardware wallets following a firmware. . .
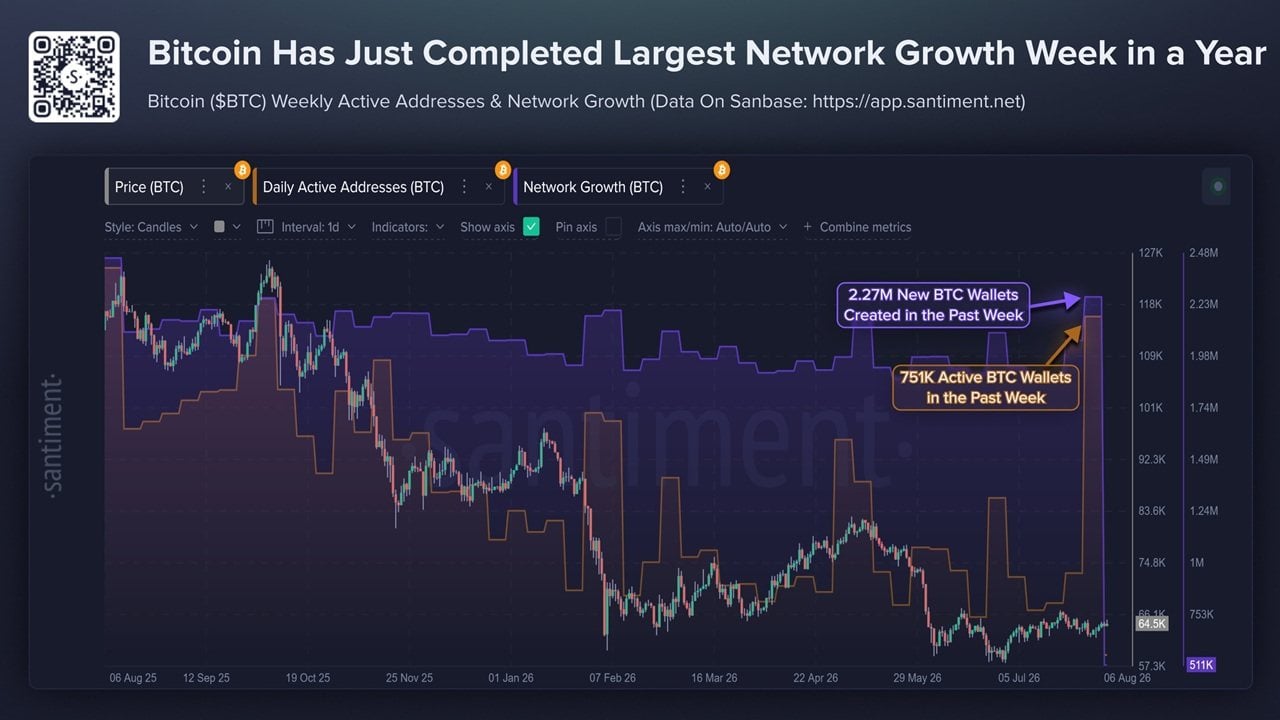
Bitcoin logged 2. 27 million new wallets and 751,000 active wallets this week, its strongest onchain activity in months, as holders raced to move funds off Coldcard hardware wallets following a firmware exploit that has drained more than $116 million. Key TakeawaysBitcoin logged 2. 27 million new wallets and 751,000 active wallets, its strongest reading in months. The spike follows a Coldcard firmware flaw that has drained more than $116 million in BTC since July 30. Exchange inflows stayed below July’s average, suggesting security moves rather than a selling wave. A Security-Driven Surge, Not a Buying SpreeSantimentput out onchain figuresthis week, describing 751,000 active wallets and 2. 27 million freshly created ones as bitcoin’s strongest network activity in months. Active addresses peaked near 978,000 on July 31, about 1. 6 times July’s daily average, before settling into a still-elevated range of roughly 751,000 per day through the first week of August, versus a July average closer to 610,000. Image source: SantimentWhat makes this spike different from a typical bull-market address boom is what’s missing, i. e. buying. Exchange inflows over the same stretch averaged about $1. 55 billion daily, actually slightly below July’s $1. 67 billion average. Wallets are multiplying and moving coins, but the money isn’t piling into exchanges to trade. That divergence suggests defensive behavior. Inside the Coldcard FlawThe trigger traces back to Coinkite’s Coldcard hardware wallets, where a firmware bug (first introduced in a March 2021 build across versions 4. 0. 1 through 4. 1. 9) routed seed-phrase generation through a software random-number generator instead of the device’s dedicated hardware entropy chip on affected Mk3 units. What should have been a 128-bit cryptographic key came out with roughly 40 bits of real randomness on the worst-affected devices, and around 72 bits on some later models. Bitcoin. com News has tracked the toll, withlosses topping $116 millionand a fourth wave of theftsstill draining walletsdays after the initial disclosure. What the Data Actually ShowsAs word spread that certain Coldcard Mk3, Mk4, Mk5 and Q devices running vulnerable firmware could have their seeds brute-forced, security-conscious holders had every reason to generate new wallets on unaffected hardware, sweep their coins to fresh addresses, and rotate away from any setup that might share the same weak-entropy flaw. That behavior alone can explain the spike in new and active wallets, paired with exchange inflows that never followed. Coinkite has since shipped a firmware fix and published an entropy hotfix disclosure detailing exactly how much randomness affected devices actually generated. Independent security researchers have also piled in with one emergency audit effort findingnearly 5,000 separate vulnerabilitiesacross hundreds of bitcoin-adjacent projects in just over a day of testing. Not a Protocol-Level ProblemExperts have been careful to draw a distinction between this incident and a flaw in bitcoin itself. Theweakness sat entirelyin how one manufacturer’s firmware generated randomness for seed phrases, a self-custody supply-chain failure rather than anything wrong with the blockchain. Geographic data added another wrinkle to the mix as researchers tracking victim wallets foundCanadian users account for roughly a quarterof the exploit’s losses, likely reflecting Coinkite’s Canadian base and a concentrated early customer footprint there. Combined with reports that the exploit brieflyfueled market anxiety around unrelated bitcoin fork proposalscirculating at the same time, the episode has become a case study in how a narrow, patchable firmware bug can still ripple into headline onchain metrics well beyond the affected device count.